
Quer melhorar o conteúdo do nó? Tente fazer uma solicitação de edição.
On May 28, 2026, IBM and its subsidiary Red Hat announced Project Lightwell, an unprecedented five billion dollar corporate commitment designed to structurally fortify the global open source software supply chain. This massive financial and operational initiative marks a fundamental paradigm shift in enterprise technology, moving away from reactive cybersecurity postures toward an active, artificial intelligence-driven defensive architecture. Backed by a dedicated task force of over twenty thousand engineers, Project Lightwell introduces a centralized, trusted enterprise clearinghouse configured to ingest, audit, and systematically patch open source code using custom frontier artificial intelligence models. The timing of this intervention addresses a structural crisis in modern enterprise infrastructure. New intelligence from the nineteenth annual Verizon Data Breach Investigations Report confirms that software vulnerabilities have officially surpassed stolen credentials as the leading primary entry point for corporate data breaches. This tactical shift by threat actors is directly driven by the democratization of adversarial artificial intelligence tools, which have compressed the operational window between vulnerability exposure and automated exploitation from months to a matter of hours. By flooding the ecosystem with automated, high-velocity scanning and exploit-generation scripts, attackers have effectively overwhelmed traditional human-centric patching cadences. Project Lightwell addresses this systemic vulnerability at its upstream root. Operating in direct collaboration with global financial institutions, including Goldman Sachs, JPMorganChase, and Bank of America, the initiative establishes a validation layer that isolates, stress-tests, and remediates open source code before it enters production environments. By deploying twenty thousand engineers to work alongside open source community maintainers, IBM and Red Hat are positioning human engineering capacity as a premium strategic differentiator. This structural intervention marks the end of the unmanaged open source era, replacing it with a heavily audited, artificial intelligence-stabilized framework that treats open source software as critical sovereign infrastructure.
The announcement of Project Lightwell by IBM and Red Hat represents a defining moment in the evolutionary timeline of enterprise software architecture. Over the past three decades, open source software has transitioned from an ideological, community-driven movement into the foundational engine of global digital commerce. Today, an estimated ninety-six percent of all commercial software applications contain open source components, with open source code making up between seventy to ninety percent of the total volume of modern codebases. However, this massive, highly distributed infrastructure has long suffered from a structural economic paradox: it is universally utilized by multi-billion-dollar enterprises but largely maintained by fractured, underfunded, and voluntary community networks.
Project Lightwell directly confronts this systemic vulnerability with a five billion dollar capitalization strategy. This initiative does not merely represent an increased expenditure on corporate cybersecurity tools; rather, it is a structural re-engineering of the global software supply chain. By establishing a centralized, trusted enterprise clearinghouse, IBM and Red Hat are inserting an authoritative validation layer between upstream, unverified open source repositories and the mission-critical production environments of global enterprise networks. This initiative represents a comprehensive, multi-layered defensive strategy designed to address the realities of modern, weaponized software exploitation.
The Vulnerability Crisis and the Death of the Credential Era
To understand the strategic necessity of Project Lightwell, one must analyze the broader shift in the cyber threat landscape that crystallized in May 2026. For nearly two decades, the consensus across corporate security departments was that human behavior represented the weakest link in defense. Phishing campaigns, social engineering schemes, and the reuse of compromised corporate credentials constituted the vast majority of initial access vectors documented by security researchers.
Data released in the nineteenth annual Verizon Data Breach Investigations Report reveals that this historic trend has permanently inverted. For the first time since the inception of the report, the exploitation of software vulnerabilities has eclipsed compromised credentials as the primary method utilized by threat actors to breach corporate perimeters. This inversion represents an operational escalation. While human-centric attacks require targeted social engineering and manual execution, software vulnerabilities allow for highly automated, non-interactive, and mass-scale exploitation.
This shift has been dramatically accelerated by the commercialization and deployment of adversarial artificial intelligence models. Threat actors are now utilizing highly specialized LLMs and automated agentic frameworks to conduct continuous, automated reconnaissance across the public IP space. These adversarial systems are capable of ingestion and semantic analysis of newly published Common Vulnerabilities and Expositions (CVEs), open source code commits, and pull requests. Once a structural flaw is identified in an upstream open source repository, these AI models can automatically synthesize functional exploit payloads and deploy them across thousands of corporate networks simultaneously.
The resulting compression of the vulnerability-to-exploit timeline has rendered traditional patch management paradigms entirely obsolete. Historically, enterprise security teams operated on a multi-week or multi-month patching cycle, allowing time for internal testing, regression analysis, and scheduled maintenance windows. In the current threat landscape, the duration between the public disclosure of a software flaw and its active exploitation has shrunk from an average of forty-five days down to a few hours. Enterprises are no longer fighting human adversaries working at human speed; they are facing automated, recursive scanning networks that exploit software flaws before corporate IT departments can even review the relevant vendor security advisories.
The Architecture of Project Lightwell
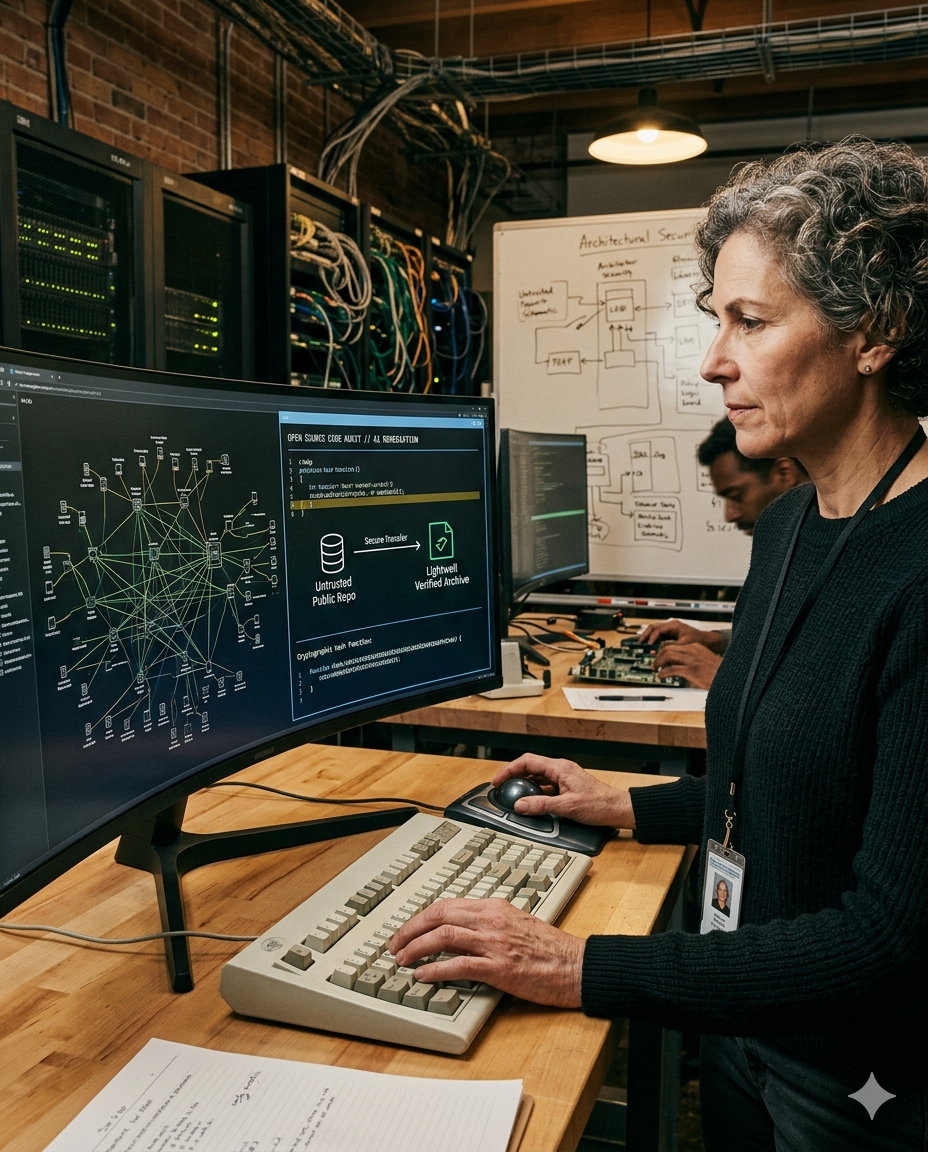
Project Lightwell counters this high-velocity threat landscape by constructing an artificial intelligence-driven, enterprise-grade clearinghouse for open source software. The operational workflow of this clearinghouse is structured around automated ingestion, semantic code auditing, continuous integration testing, and automated patch distribution.
At the core of Project Lightwell are frontier artificial intelligence models specifically trained on massive semantic datasets of software code, historical vulnerability reports, AST (Abstract Syntax Tree) configurations, and runtime execution logs. Unlike legacy static application security testing (SAST) tools, which rely on rigid, rule-based signature matching and generate debilitating rates of false positives, the Lightwell AI engine executes deep contextual analysis. It evaluates code architecture similarly to an advanced human code auditor, understanding how data flows across complex, multi-layered dependencies and identifying deep-seated logic flaws, memory management errors, and race conditions that evade traditional testing matrices.
When an upstream open source library—such as a widely utilized logging framework, cryptographic utility, or data serialization package—pushes an update, the Lightwell clearinghouse automatically clones the repository into an isolated, high-performance sandbox environment. The frontier AI models immediately subject the code to automated code review, identifying potential security vectors and structural anomalies. Simultaneously, the system generates targeted fuzzing matrices—inputs designed to induce edge-case failures—to stress-test the component under extreme operational simulation.
If a vulnerability is detected, the Project Lightwell infrastructure shifts from passive detection to active remediation. The platform's generative AI models produce a targeted, syntactically correct security patch designed to eliminate the risk vector without altering the core functional behavior of the underlying software library. This automated patch is then instantly deployed into an automated regression testing environment that replicates thousands of enterprise deployment configurations, ensuring that the modification does not introduce breaking changes or performance degradation.
Once validated, the secure, hardened patch is introduced into the Lightwell Enterprise Supply Chain Feed. Corporate subscribers can ingest these pre-validated, enterprise-grade open source components directly into their internal artifact repositories (such as Nexus or Artifactory) through automated continuous integration and continuous deployment (CI/CD) pipelines. This architecture effectively insulates the enterprise from the volatile upstream open source ecosystem, providing an audited, secure, and continuously patched mirror of global open source software.
The Strategic Value of Human Capital at Scale
A particularly striking aspect of the Project Lightwell announcement is the commitment of a global engineering force exceeding twenty thousand personnel. In an economic environment where the technology sector has extensively leveraged artificial intelligence as a mechanism to downsize engineering headcount and compress payroll expenses, IBM and Red Hat are executing a deliberate counter-strategy. They are positioning human engineering capacity as a premium strategic asset and a critical market differentiator.
The integration of twenty thousand software and security engineers represents the vital human-in-the-loop validation layer necessary to scale artificial intelligence operations safely. While AI models possess unmatched velocity in processing petabytes of source code and identifying anomalies, they lack the high-level contextual reasoning required to assess complex business logic and architectural risks uniquely found in bespoke enterprise environments.
The Lightwell engineering force operates across three distinct operational vectors:
Upstream Community Maintenance
A significant portion of the twenty thousand engineers will be assigned directly to upstream open source projects, working collaboratively within existing foundation structures such as the Linux Foundation, Apache Software Foundation, and Cloud Native Computing Foundation. Rather than allowing these critical digital commons to languish due to a lack of resources, IBM and Red Hat are injecting highly paid, expert engineering hours directly into the community. These engineers will focus extensively on core security health, refactoring legacy codebases, implementing memory-safe programming languages, and establishing rigid access controls over repository governance to prevent malicious maintainer takeovers.
High-Volume Triage and Validation
The AI-driven clearinghouse will continuously generate vulnerability flags, automated patch suggestions, and telemetry reports. The engineering force acts as a triage layer, separating genuine architectural risks from complex false positives. This human verification loop continuously feeds back into the frontier AI training pipelines, refining the models' contextual understanding and drastically reducing error rates over time.
Secure Patch Development and Lifecycle Management
When critical zero-day vulnerabilities emerge in the wild, the engineering force is deployed into rapid-response units. These groups work in parallel with automated AI generation systems to build, validate, and sign enterprise patches. Crucially, they provide long-term lifecycle management for these patches, ensuring that backported security fixes remain compatible with legacy enterprise software versions that corporate clients cannot easily or immediately upgrade.
The Coalition of Early Adopters
The structural viability of Project Lightwell is heavily reinforced by its launching coalition of early corporate adopters. Rather than debuting this platform as an unproven commercial experiment, IBM and Red Hat have secured immediate integration commitments from the world’s most heavily regulated and systemically critical financial enterprises. The initial cohort includes Bank of America, BNY, Citi, Goldman Sachs, JPMorganChase, Mastercard, Morgan Stanley, Royal Bank of Canada, State Street, Visa, and Wells Fargo.
The participation of these tier-one financial institutions is highly significant for two primary reasons: data volume and regulatory gravity. The global financial system represents the absolute apex of cyber-adversarial targeting. By deploying Project Lightwell across these vast, complex, and highly secure infrastructure environments, IBM and Red Hat will immediately gain access to high-fidelity, real-world operational telemetry. The insights gained from tracking how open source dependencies behave inside the core clearing, payment, and trading architectures of these institutions will actively shape and refine how vulnerabilities are identified and remediated at scale.
Furthermore, the financial services industry operates under the most stringent digital sovereignty and operational resilience mandates globally, such as the Digital Operational Resilience Act (DORA) in Europe and evolving SEC cybersecurity disclosure mandates in the United States. By securing the endorsement of these institutions, IBM and Red Hat are establishing Project Lightwell as the de facto compliance standard for software supply chain security. If a clearinghouse model can successfully satisfy the risk parameters of Goldman Sachs and JPMorganChase, it creates an immense gravitational pull that will inevitably compel other highly regulated sectors—such as defense, aerospace, healthcare, and telecommunications—to adopt the identical architecture.
The Shadow AI Vector and Internal Data Leakage
While Project Lightwell builds a sophisticated external defense system around incoming software components, it arrives at a time when enterprise perimeters are being severely compromised from within by an adjacent phenomenon: the explosion of shadow artificial intelligence. Data from regional technology assessments in May 2026 indicates that corporate employee utilization of unapproved consumer artificial intelligence tools has skyrocketed from fifteen percent to forty-five percent within a single calendar year.
This surge in shadow AI introduces an acute data leakage risk vector that intersects directly with software supply chain security. Corporate developers, eager to accelerate their productivity in the face of compressed timelines, are routinely copying proprietary corporate source code, internal API schemas, and sensitive algorithmic structures, and pasting them into public, consumer-facing LLM interfaces to assist with debugging or optimization. In doing so, they inadvertently expose intellectual property and internal corporate vulnerabilities to third-party training data ingestions.
This internal behavioral shift complicates the software security model. An enterprise can implement rigorous code auditing at its outer boundary via Project Lightwell, but if its internal developers are concurrently leaking corporate software logic into external AI ecosystems, the overall risk posture remains highly volatile. Threat actors can theoretically exploit consumer LLM training data loops or target the less secure repositories of third-party AI vendors to discover structural blueprints of enterprise networks. Consequently, the deployment of Project Lightwell will require enterprises to enforce rigid, policy-driven programmatic controls over internal developer environments, effectively mandating that any AI-assisted coding occur strictly within isolated, enterprise-controlled, and audited local models.
Geopolitical Implications and Digital Sovereignty
Beyond its immediate technical and commercial ramifications, Project Lightwell represents a major escalation in the ongoing pursuit of digital sovereignty. In the current geopolitical climate, software code is no longer viewed merely as an asset of commercial utility; it is increasingly recognized as an arena of state-level kinetic and asymmetric conflict. Upstream open source repositories represent an incredibly attractive vector for state-sponsored advanced persistent threats (APTs) seeking to conduct systemic, long-term espionage or embed latent kill-switches within critical national infrastructure.
Recent history is replete with instances where state-aligned actors spent years quietly contributing to open source projects, gradually building trust within the community, solely to insert sophisticated, obfuscated backdoors into foundational utilities used by governments and enterprises worldwide. By establishing a well-capitalized, highly scrutinized corporate clearinghouse, IBM and Red Hat are effectively imposing a corporate checkpoint on the global digital commons.
This intervention inevitably alters the power dynamics of open source governance. Historically, open source has been explicitly anti-nationalist and decoupled from centralized corporate hegemony, operating on a philosophy of borderless, democratic collaboration. Project Lightwell introduces a structural bifurcation. On one side remains the raw, unverified, and completely open upstream ecosystem; on the other sits a heavily fortified, corporate-curated, and western-enterprise-aligned software supply chain.
While this model provides the deterministic security and operational continuity that sovereign states and critical enterprises demand, it also concentrates immense regulatory and structural power within the corporate apparatus of IBM and Red Hat. The clearinghouse will effectively dictate which code changes are deemed safe for global commerce, turning software validation into an implicit form of geopolitical border control.
The New Economics of Software Engineering
Project Lightwell fundamentally reconfigures the economic calculus underlying software development and enterprise software licensing. For the past decade, the prevailing trend among enterprise software vendors has been the monetization of software features, user seats, and SaaS-delivered cloud hosting. However, as generative artificial intelligence models commoditize the actual production of code, the market value of standard software features is rapidly trending toward zero. Anyone can now utilize an agentic AI system to generate functional application code on demand.
The true premium scarcity in the era of ubiquitous, AI-generated code is not the code itself, but the validation, security, and long-term maintenance of that code. By committing five billion dollars to Project Lightwell, IBM and Red Hat are executing a profound strategic pivot to capture this new economic reality. They are shifting their primary monetization engine away from software delivery and toward software verification.
The business model underpinning Project Lightwell relies on commercial subscription frameworks that integrate directly into the deployment pipelines of enterprise customers. Enterprises are no longer paying for the underlying open source code—which remains free and public—but are instead paying a premium insurance and validation tariff to ensure that the code entering their environments has been cleansed by the Lightwell AI engine and verified by Red Hat engineers. This converts cybersecurity from an internal, fragmented cost center into a predictable, externalized utility subscription.
Furthermore, this model creates an intensely high barrier to entry for potential competitors. Replicating a twenty thousand person global engineering force and training specialized frontier models on proprietary enterprise telemetry requires a capital allocation that very few technology companies can sustain. IBM and Red Hat are effectively establishing an operational moat that positions their ecosystem as the definitive, sovereign utility provider for enterprise-grade open source software.
The Long-Term Trajectory of Automated System Auditing
Looking toward the horizon, Project Lightwell represents the foundational scaffolding for an era characterized by entirely autonomous system auditing. As the models driving the clearinghouse evolve from identifying localized software flaws to comprehending macro-architectural systems, the nature of enterprise IT management will fundamentally transform.
In this future paradigm, software systems will no longer be viewed as static architectural constructs that require periodic manual reviews and scheduled upgrades. Instead, enterprise software architectures will function as living, evolving digital organisms. These organisms will continuously self-audit, automatically identifying internal logic bottlenecks, tracking evolving threat landscapes in real-time, and synthesizing their own defensive modifications without human intervention.
The historical division between software development, system administration, and cybersecurity will completely dissolve into unified, continuous optimization loops managed by specialized AI agents. Human engineers will shift permanently away from the manual syntax level of writing code, moving instead into hyper-strategic roles centered around policy definition, systemic risk budgeting, and ethical governance.
Project Lightwell is the catalyst for this transition. By capitalizing this automated defensive layer at an unprecedented scale, IBM and Red Hat are establishing the necessary infrastructure to prevent the modern digital economy from collapsing under the weight of its own unmanaged complexity. It is a bold acknowledgment that in an era dominated by high-velocity, automated digital threats, the only viable defense is an equally automated, systemically integrated, and heavily capitalized intelligence architecture.
1
0
0
0

Comentários